European Blood Banks Targeted in Wave of Remote Refrigeration Cyberattacks
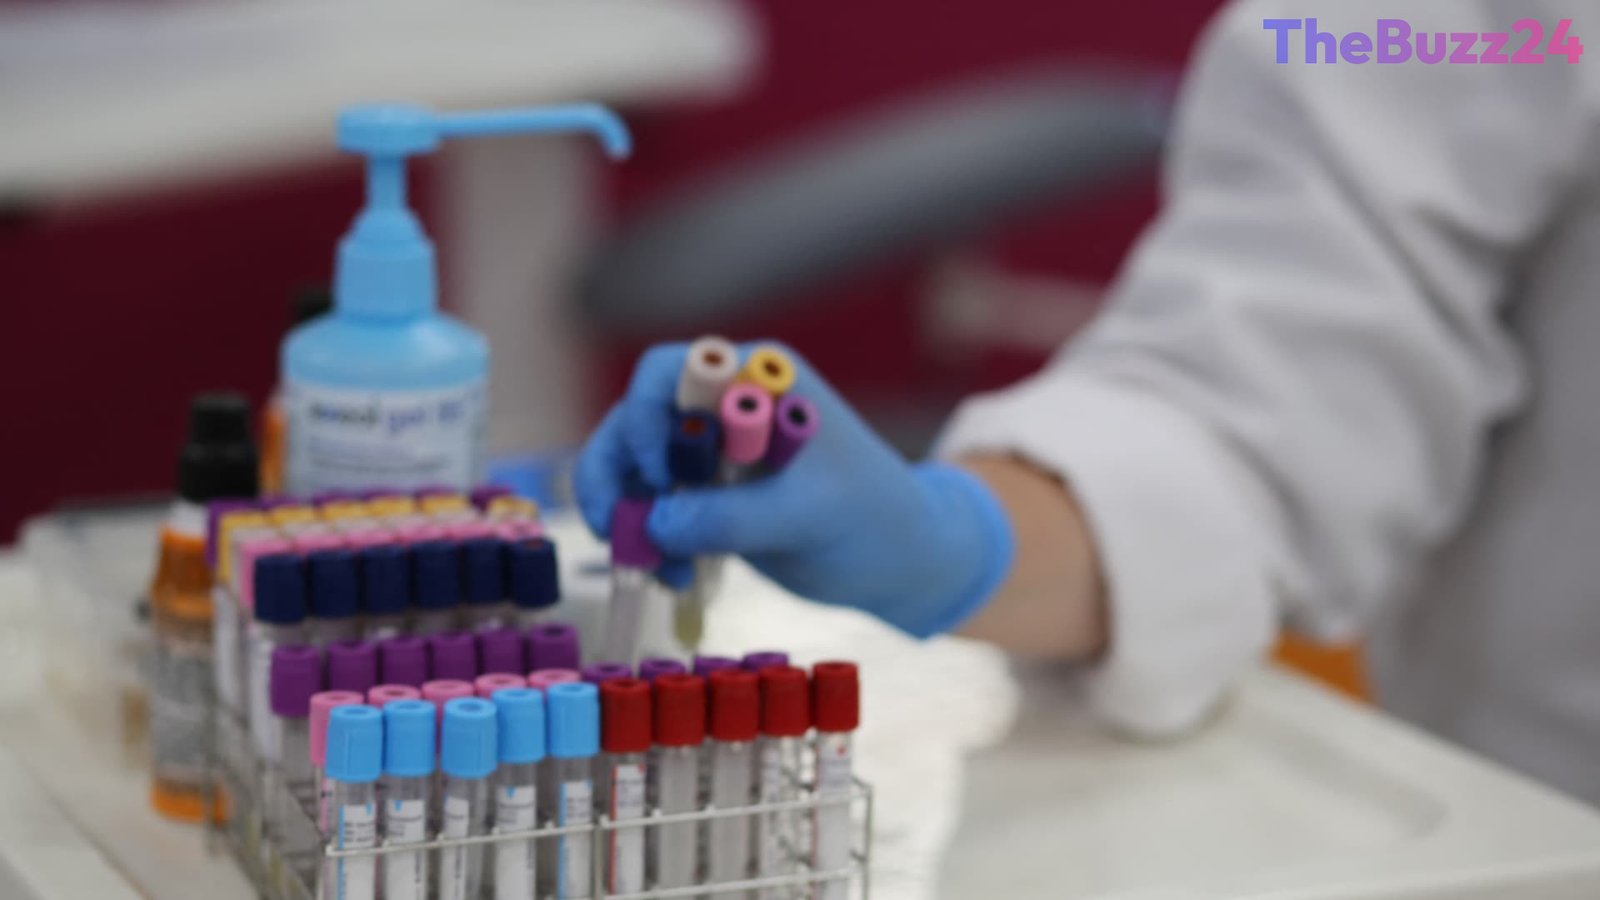
Critical medical infrastructure has fallen victim to a sweeping campaign of cyberattacks targeting commercial refrigeration systems across Europe. The French Blood Establishment (EFS) confirmed that cold storage units containing vital blood products and biological samples were remotely breached, resulting in dangerously elevated internal temperatures.
The sophisticated cyber intrusions, which mirror similar recent attacks against hundreds of supermarkets throughout France, Belgium, Sweden, and Finland, targeted external providers operating cold storage infrastructure for the EFS. Hackers manipulated temperature and defrost thresholds to dangerously high levels in an apparent attempt to compromise stored plasma, blood reserves, and medical samples destined for healthcare facilities.
Fortunately, rapid-response surveillance and alarm systems detected the thermal anomalies before any irreversible damage occurred. Affected equipment was swiftly isolated, brought back under control, or taken offline, while endangered samples were successfully relocated to secure facilities. The EFS reported zero loss of blood products and confirmed no adverse health impacts stemming from the security breach.
In the wake of the incident, the EFS has partnered closely with the French National Cybersecurity Agency (ANSSI) and the Ministry of Health to reinforce digital defenses and heighten monitoring protocols across all storage nodes. While the immediate crisis has been neutralized, authorities remain on high alert as investigations into the broader European refrigeration hacking campaign continue.
Key Takeaways
- Cold storage units storing blood products and plasma across multiple French sites were remotely hacked by altering temperature thresholds.
- Rapidly triggered surveillance alarms and emergency protocols prevented the loss of any blood products or biological samples.
- The incident is part of a wider European cyber campaign that previously targeted supermarket refrigeration systems in several countries.
Editor’s Analysis & Impact
The targeting of blood banks via connected refrigeration units highlights a deeply concerning evolution in cyber warfare and extortion tactics, shifting focus from traditional IT networks to Internet of Things (IoT) and operational technology (OT). While this particular incident resulted in no loss of life or inventory thanks to robust monitoring systems, it serves as a stark wake-up call for the healthcare and biomedical sectors. Supply chain vulnerabilities involving third-party vendors represent a massive vector of risk. Moving forward, critical infrastructure operators must mandate rigorous zero-trust frameworks, advanced anomaly detection, and secure air-gapped backups for all temperature-sensitive medical storage to prevent potentially catastrophic disruptions to public health networks.
Frequently Asked Questions
Q: Were any blood products lost during the cyberattack?
A: No, surveillance systems detected the temperature anomalies quickly, allowing staff to secure the equipment, transfer samples safely, and prevent any loss of blood products.
Q: How were the cold storage units compromised?
A: Hackers remotely accessed refrigeration monitoring and control systems operated by external providers, setting temperature and defrost thresholds to excessively high levels.
Q: Which agencies are investigating the breach?
A: The French Blood Establishment is coordinating its response and investigation with the French National Cybersecurity Agency (ANSSI) and the Ministry of Health.
AI Disclosure: This article is based on verified data and official reports. Our Team and AI have cross-referenced every financial detail with primary sources to ensure total accuracy.
More from this Category