The ‘ClickFix’ Threat: How Hackers Are Tricking Users Into Compromising Their Own Devices
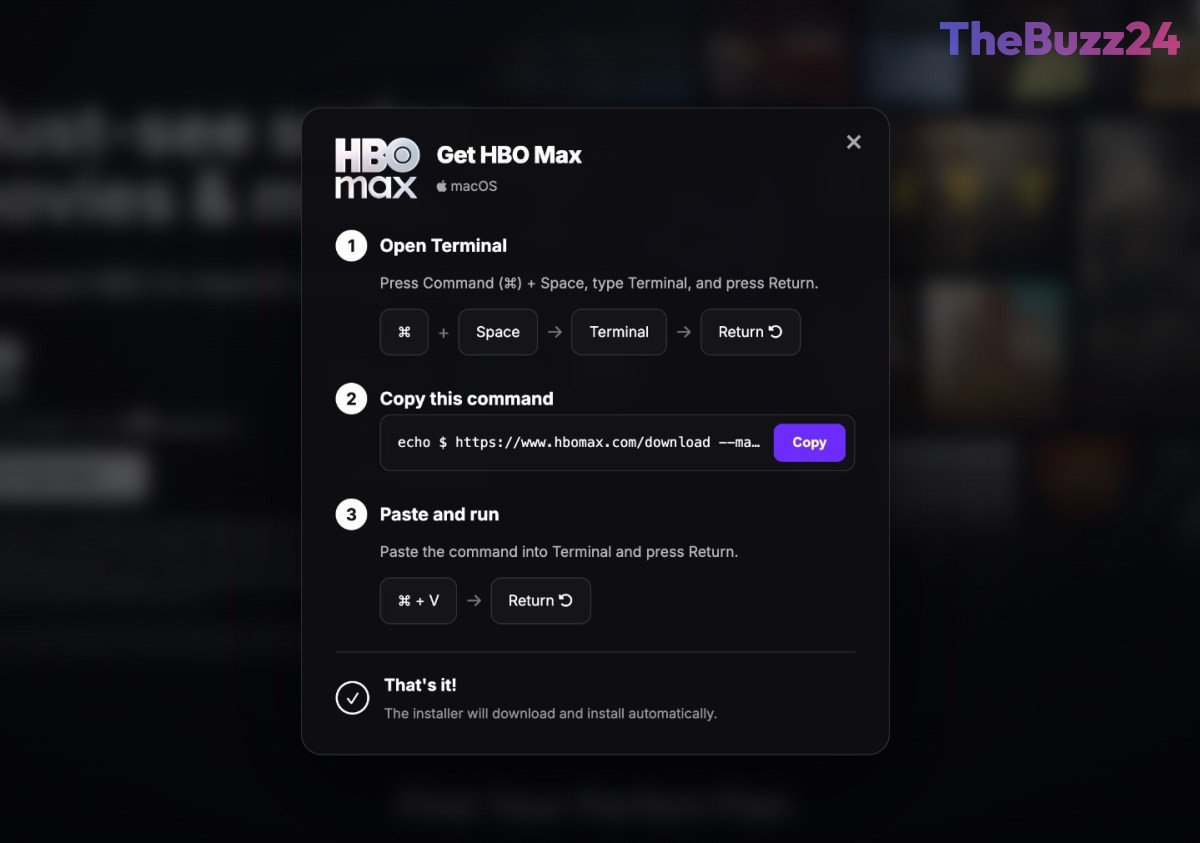
A sophisticated cybersecurity threat known as ‘ClickFix’ is rapidly gaining traction, targeting both Mac and Windows users by manipulating them into executing malicious commands on their own machines. These attacks typically begin on compromised or fraudulent websites, where users are presented with a deceptive prompt disguised as a CAPTCHA or an anti-bot verification tool. When a user interacts with the prompt, they are instructed to copy and paste a specific string of text into their system’s Terminal or Command Prompt, effectively granting the attacker full control over the device.
Once the command is executed, the system unwittingly installs advanced info-stealing malware. This software is designed to harvest sensitive data, including saved passwords, active session cookies, and cryptocurrency wallet credentials. Because the malicious activity is initiated through the operating system’s native command-line interface, it often bypasses traditional antivirus and endpoint security software that typically monitors for suspicious file downloads rather than legitimate system commands.
Recent campaigns have demonstrated the reach of these tactics, including a high-profile incident where a compromised official Reddit account for HBO Max was used to distribute malicious advertisements. While platforms like Reddit have taken steps to lock compromised accounts and remove fraudulent links, the incident highlights the vulnerability of even well-known brands to social engineering. Security experts advise that users should never copy and paste commands from unverified sources into their system terminals, and organizations are encouraged to restrict access to command-line tools for non-technical staff to mitigate the risk of such exploits.
Key Takeaways
- ClickFix attacks trick users into manually executing malicious code via their computer's Terminal or Command Prompt.
- The malware is designed to steal passwords, account access, and cryptocurrency wallets while bypassing standard antivirus software.
- Hackers are increasingly using compromised social media and advertising accounts to lend legitimacy to their malicious links.
Editor’s Analysis & Impact
The rise of ClickFix attacks represents a dangerous shift in social engineering, moving away from traditional phishing toward ‘user-assisted’ exploitation. By leveraging the user’s own administrative privileges, attackers bypass the primary defense layers of modern operating systems. This trend underscores a critical gap in consumer-grade cybersecurity: the assumption that users understand the risks associated with command-line interfaces. As these attacks become more frequent, we expect to see a push for stricter enterprise-level controls on terminal access and potentially new OS-level warnings when users attempt to paste complex scripts into system consoles. The industry must pivot toward educating users that ‘copy-pasting’ is a high-risk activity, regardless of how legitimate a website appears to be.
Frequently Asked Questions
Q: What is a ClickFix attack?
A: A ClickFix attack is a social engineering tactic where users are tricked into copying and pasting malicious code into their computer's Terminal or Command Prompt, which then installs malware on their system.
Q: How can I protect myself from ClickFix?
A: Never copy and paste commands from websites into your Terminal or Command Prompt unless you are an expert and fully understand what the code does. Additionally, ensure your security software is updated and avoid clicking on suspicious advertisements, even if they appear on reputable platforms.
AI Disclosure: This article is based on verified data and official reports. Our Team and AI have cross-referenced every financial detail with primary sources to ensure total accuracy.
More from this Category