Bitget Faces Uphill Battle to Recover $388M Following Sophisticated Cyberattack
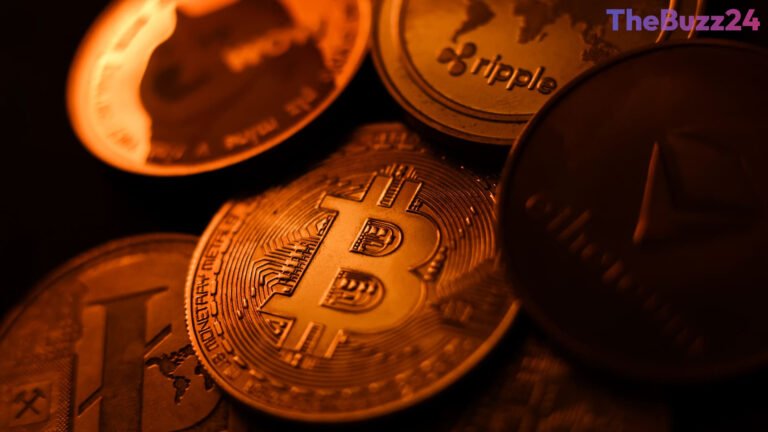
Cryptocurrency exchange Bitget has successfully frozen roughly $1.1 million of the nearly $388 million pilfered during a recent major security breach. Despite ongoing recovery efforts and collaboration with digital forensics experts, company leadership acknowledges that retrieving a substantial portion of the stolen digital assets remains unlikely, mirroring historical recovery rates seen across the broader cryptocurrency sector.
The sophisticated cyber incident, which unfolded through compromised third-party security vendors, prompted immediate defensive measures from the platform. Investigators from Mandiant and SlowMist revealed that the perpetrators exploited an unknown zero-day vulnerability to gain privileged internal access, bypassing standard withdrawal safeguards without compromising private keys. Although user balances were shielded from direct financial losses, the breach severely depleted the platform’s dedicated insurance reserve.
In response to the deficit, executive leadership utilized internal company capital to restore the user protection fund to over $300 million, ensuring it remains transparently verifiable on-chain. Operations are steadily returning to normal as the exchange resumes standard withdrawal services for major digital assets like bitcoin, ether, and USDT, while reinforcing its infrastructure against future vulnerabilities.
Key Takeaways
- Bitget has managed to freeze only $1.1 million out of the nearly $388 million stolen in the recent cyberattack.
- The exchange replenished its user protection fund back to over $300 million using internal capital reserves.
- Investigations by security firms revealed the hackers exploited a zero-day vulnerability in third-party security products to gain internal access.
Editor’s Analysis & Impact
The massive $388 million breach at Bitget underscores the persistent and evolving vulnerability of centralized cryptocurrency exchanges, particularly regarding supply chain risks involving third-party vendors. While the platform’s swift action to absorb the financial blow and replenish its user protection fund helps maintain immediate customer trust and liquidity, the low projected recovery rate highlights a broader systemic issue within the digital asset industry: stolen funds remain remarkably difficult to trace and retrieve once funneled through sophisticated laundering networks. Moving forward, this incident will likely trigger tighter regulatory scrutiny on how exchanges vet third-party software integrations and manage operational security barriers. Platforms must increasingly demonstrate robust, transparent reserve backing and proactive risk management to survive in an environment where cyber threats are becoming progressively sophisticated.
Frequently Asked Questions
Q: Were user account balances affected by the Bitget hack?
A: No, user account balances remained unaffected, and the financial impact was absorbed directly by Bitget using its own capital reserves rather than being passed on to customers.
Q: How did the attackers gain access to Bitget's systems?
A: According to investigative reports, the attackers exploited a zero-day vulnerability in third-party security products to obtain privileged internal access and bypass normal withdrawal processes without stealing private keys.
Q: How much money was the user protection fund restored to?
A: Bitget replenished its protection fund back up to more than $300 million using its own reserves after it was drawn down following the theft.
AI Disclosure: This article is based on verified data and official reports. Our Team and AI have cross-referenced every financial detail with primary sources to ensure total accuracy.
More from this Category