The Chilling Reality: Cyber Threats to Smart Devices and Supply Chains
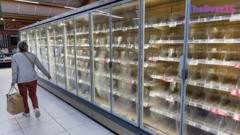
A wave of suspected cyber-attacks has recently impacted supermarkets across Europe, specifically targeting their refrigeration and freezer systems. These incidents have ignited significant concern regarding the inherent vulnerabilities of internet-connected hardware, spanning from sophisticated industrial machinery to common domestic appliances. While smart devices like fridges, central heating units, and even washing machines offer convenience through remote control, their online connectivity simultaneously exposes them to potential exploitation by malicious actors. Although major brands typically invest heavily in securing their technology, past vulnerabilities, such as a 2015 exploit in a Samsung smart fridge that allowed internet traffic interception, underscore the persistent risks. However, there is currently no evidence suggesting that domestic appliances are the direct targets of the recent supermarket cyber-attacks.
Cybersecurity experts are calling for more robust measures to safeguard these connected devices. Ciaran Martin, former chief executive of the UK’s National Cyber Security Centre (NCSC), emphasized the need for “big tech” to deliver safer products. He also advised consumers to diligently update their devices and enable multi-factor authentication whenever possible. In response to growing threats, the UK introduced legislation in April 2024, mandating minimum cybersecurity standards for certain consumer smart devices, including requirements for passwords and security updates. While the NCSC is collaborating with international partners to investigate the supermarket incidents and has not identified any direct impact on the UK, researchers from UK Cyber Defence have alarmingly identified over 800 refrigeration and building-control interfaces linked to British retailers that are publicly accessible online, potentially exposing them to attackers exploiting weak passwords or software flaws. The British Retail Consortium’s chief executive, Helen Dickinson, confirmed that cyber incidents are a major concern for retailers, who are actively sharing intelligence with the NCSC to bolster their defenses.
The implications of these attacks extend far beyond retail, raising critical questions about the security of broader infrastructure. Past ransomware attacks, such as those targeting UK supermarkets M&S and the Co-op, have already demonstrated how cyber intrusions can disrupt food supply chains, leading to empty shelves. Tom Hegel, a researcher at cybersecurity firm SentinelOne, stressed the importance of retailers clarifying who “owns” the security of their equipment, not just who repairs it. He warned that once attackers gain control, legitimate functions like defrosting can be weaponized, potentially destroying physical stock rather than merely interrupting computer systems. Concerns also encompass industrial control systems, vehicles, and utility networks. A 2015 demonstration, where researchers remotely hacked a Jeep via its internet-connected entertainment system, prompted significant improvements in vehicle security. While UK utilities are generally adept at securing their mobile-connected monitoring equipment, experts like Ken Munro highlight varying global standards and particular worries about smaller, underfunded utility companies relying on older, vulnerable infrastructure. Olivier Daloy, a cybersecurity expert at Zscaler, cautioned that without proper protections, any internet-connected factory or equipment—from car manufacturers to electricity grids or transport systems—could face similar, severe risks.
Key Takeaways
- European supermarkets faced cyber-attacks targeting refrigeration systems, highlighting widespread vulnerabilities in internet-connected devices.
- Experts emphasize the need for manufacturers to enhance device security, consumers to update software, and retailers to clarify ownership of equipment security.
- The incidents raise broader concerns about the security of industrial control systems, vehicles, and critical infrastructure, underscoring the potential for physical disruption from cyber threats.
Editor’s Analysis & Impact
The recent cyber-attacks on European supermarkets underscore a critical and escalating threat to interconnected systems across various industries. This incident will likely accelerate the demand for more robust cybersecurity solutions in retail, logistics, and manufacturing sectors. We can anticipate increased regulatory pressure on manufacturers to embed security by design in IoT devices, similar to the UK’s new legislation. The future outlook points towards a greater convergence of IT and operational technology (OT) security, as the line between digital and physical disruption blurs. Broader implications include potential supply chain instability and a heightened awareness that cyber threats can directly impact essential services and physical assets, necessitating a proactive, holistic approach to national and international cybersecurity strategies.
Frequently Asked Questions
Q: What kind of devices are considered "smart devices" or "internet-connected hardware"?
A: These include a wide range of consumer appliances like fridges, central heating systems, and washing machines, as well as industrial machinery, vehicles, and equipment used in power plants and water networks, all capable of connecting to the internet for remote control or monitoring.
Q: What are the main risks associated with these vulnerabilities?
A: Beyond data interception, the primary risk is malicious actors gaining control over physical systems. This could lead to disruption of services (like supermarket stock issues), damage to physical assets (e.g., destroying stock by changing freezer settings), or even compromise critical infrastructure like power grids and water supplies.
Q: What steps are being taken to address these security concerns?
A: Governments, like the UK, are implementing laws requiring minimum cybersecurity standards for manufacturers. Experts advise consumers to keep devices updated and use multi-factor authentication. Industry bodies and cybersecurity firms are working with retailers and utilities to share intelligence and strengthen defenses.
AI Disclosure: This article is based on verified data and official reports. Our Team and AI have cross-referenced every financial detail with primary sources to ensure total accuracy.
More from this Category